IT Service Providers: DevSecOps Meets Compliance
Cloud providers, MSPs, and data centers may fall under NIS2 as digital infrastructure, with strict requirements for availability and security.
Critical Assets in the IT Industry
These systems are in the focus of NIS2
Server Infrastructure
Physical and virtual servers, container platforms, Kubernetes clusters.
Network Components
Routers, switches, firewalls, load balancers. Backbone of your services.
Storage Systems
SAN, NAS, object storage. Securely storing customer data.
Management Platforms
RMM tools, ticket systems, monitoring. Privileged customer access.
Typical Risks for IT Service Providers
Why you are particularly in the crosshairs of attackers
Supply Chain Attacks
One compromised MSP = access to hundreds of customers (SolarWinds, Kaseya).
Credential Theft
Admin credentials for customer systems are gold for attackers.
DDoS Attacks
Availability is your core business. Outages affect all customers.
Physical Risks
Power failure, cooling, physical access control in the data center.
Key Measures for IT Companies
Art. 21 NIS2 for digital infrastructure
Risk Analysis & ISMS
Establish comprehensive risk management per ISO 27001 or equivalent national framework.
Incident Response
24/7 SOC or SIEM with clear escalation paths. Notify customers about incidents.
Business Continuity
Geo-redundancy, disaster recovery, documented RTO/RPO for all services.
Supply Chain Security
Assess your subcontractors and cloud providers. SBOM for software.
Secure Development
DevSecOps pipeline, SAST/DAST, container scanning, dependency checks.
Quick Wins for IT Service Providers
- Test and validate DDoS mitigation
- Segment customer access (no shared admin)
- Enable MFA for all management platforms
- Implement Privileged Access Management
- Aim for recognized cloud security certification (e.g. ISO 27017, SOC 2, or national equivalents)
- Clarify contractual security requirements with customers
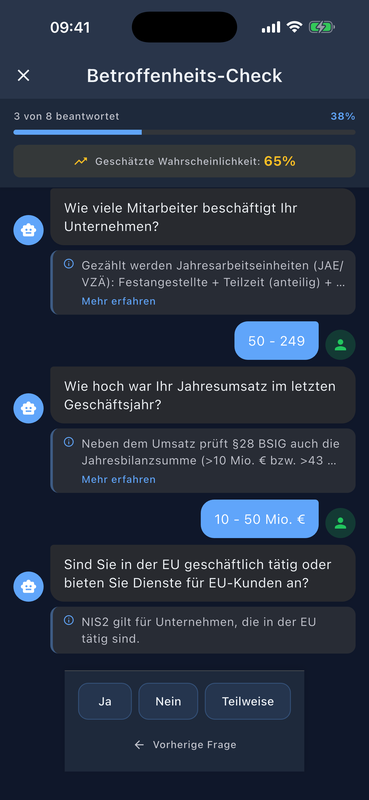
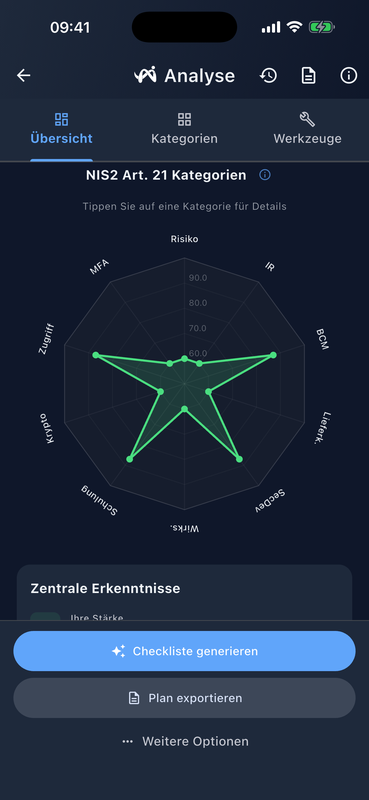
NIS2 Compliance for IT Companies
Check your applicability in 2 minutes and receive a personalized action plan.
Start Free Check